Azure logs: Grafana Alloy
Complexity: Flexible | Infrastructure: Linux, Windows, or MacOS VM | Latency: Configurable
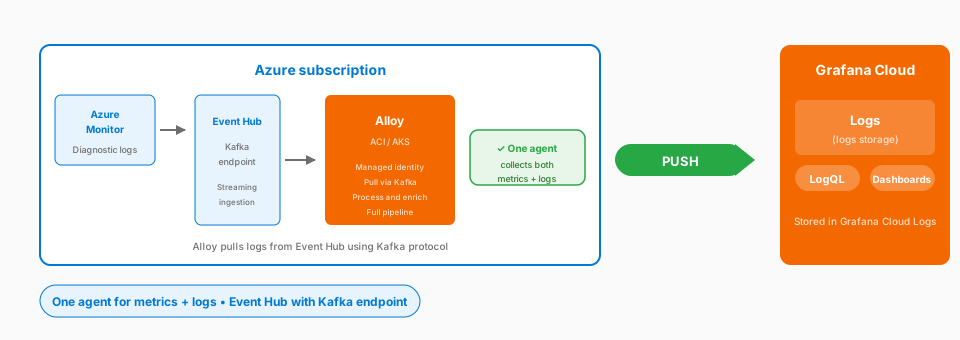
Azure Monitor streams log data to an Event Hubs namespace with a Kafka endpoint. Alloy pulls the logs using the Kafka protocol and forwards them to Grafana Cloud Logs. Its pipeline can parse, filter, relabel, and enrich logs first. If you already deployed Alloy for metrics, the same deployment can collect logs.
Considerations
- Event Hub ingestion over the Kafka protocol
- Full processing pipeline for parsing, filtering, and enrichment
- Managed identity authentication
- One deployment for both metrics and logs
- Alloy infrastructure to deploy, maintain, and update
- Event Hubs namespace must be Standard or Premium so the Kafka endpoint is available
When to use
- Complex processing needs
- Event Hub log sources
- Combined metrics + logs collection
Documentation
View the Azure Alloy logs documentation.