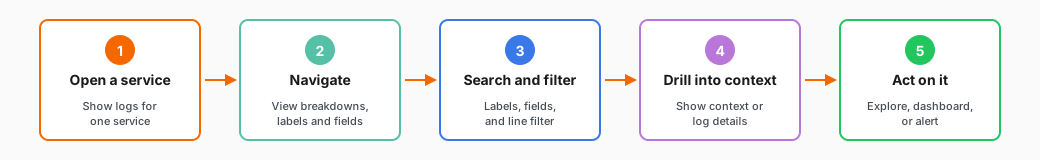
Open a service, filter, then continue in Explore or a dashboard
Estimated time: 2 min
The log investigation workflow
A typical investigation moves through five steps. You can skip a step or go back.
Step
What you do
What you get
Open a service
Select Drilldown > Logs. The overview lists services by log volume. Select Show logs
That service’s log lines on the Logs tab
Break the volume down
Open Labels or Fields. Open Patterns when pattern ingestion is enabled
Log volume for each label or field. Patterns use the previous three hours of logs
Filter
On Labels, select Select or Include. On Fields, select Include or Add to filter to narrow the lines. Select on a field shows a breakdown of its values. Or type a line filter
A smaller set of log lines from a filter, or the values of one field
Read one line
Open the log line menu and select Show context or Show log details
The lines before and after it, or its labels and fields
Continue
On a panel menu, select Explore, Add to Dashboard, or Create alert
The same selections as a LogQL query in Explore, a dashboard panel, or an alert rule
Add to Dashboard, Create alert, and Explain in Assistant appear only when that Grafana feature is available.
Explore opens Grafana Explore with a query based on the selections you made in Logs Drilldown.